
Unbiased headlines. Facts, not spin.
Unbiased Headlines is an independently owned news organization. We bring you the facts, not opinions, written fresh from 110+ named sources. Sources linked so you can verify it yourself.
 health
Notable (6/10)
Event date: November 11, 2026 ·
Unapproved AI Tool Exposed 3,182 Johns Hopkins Bayview Patients; Survey Says 91% of Health Organizations Can't Verify What AI They Run
The latest healthcare data breach did not come from a ransomware crew or a foreign hacker. It came from an employee with a spreadsheet and a public AI tool.
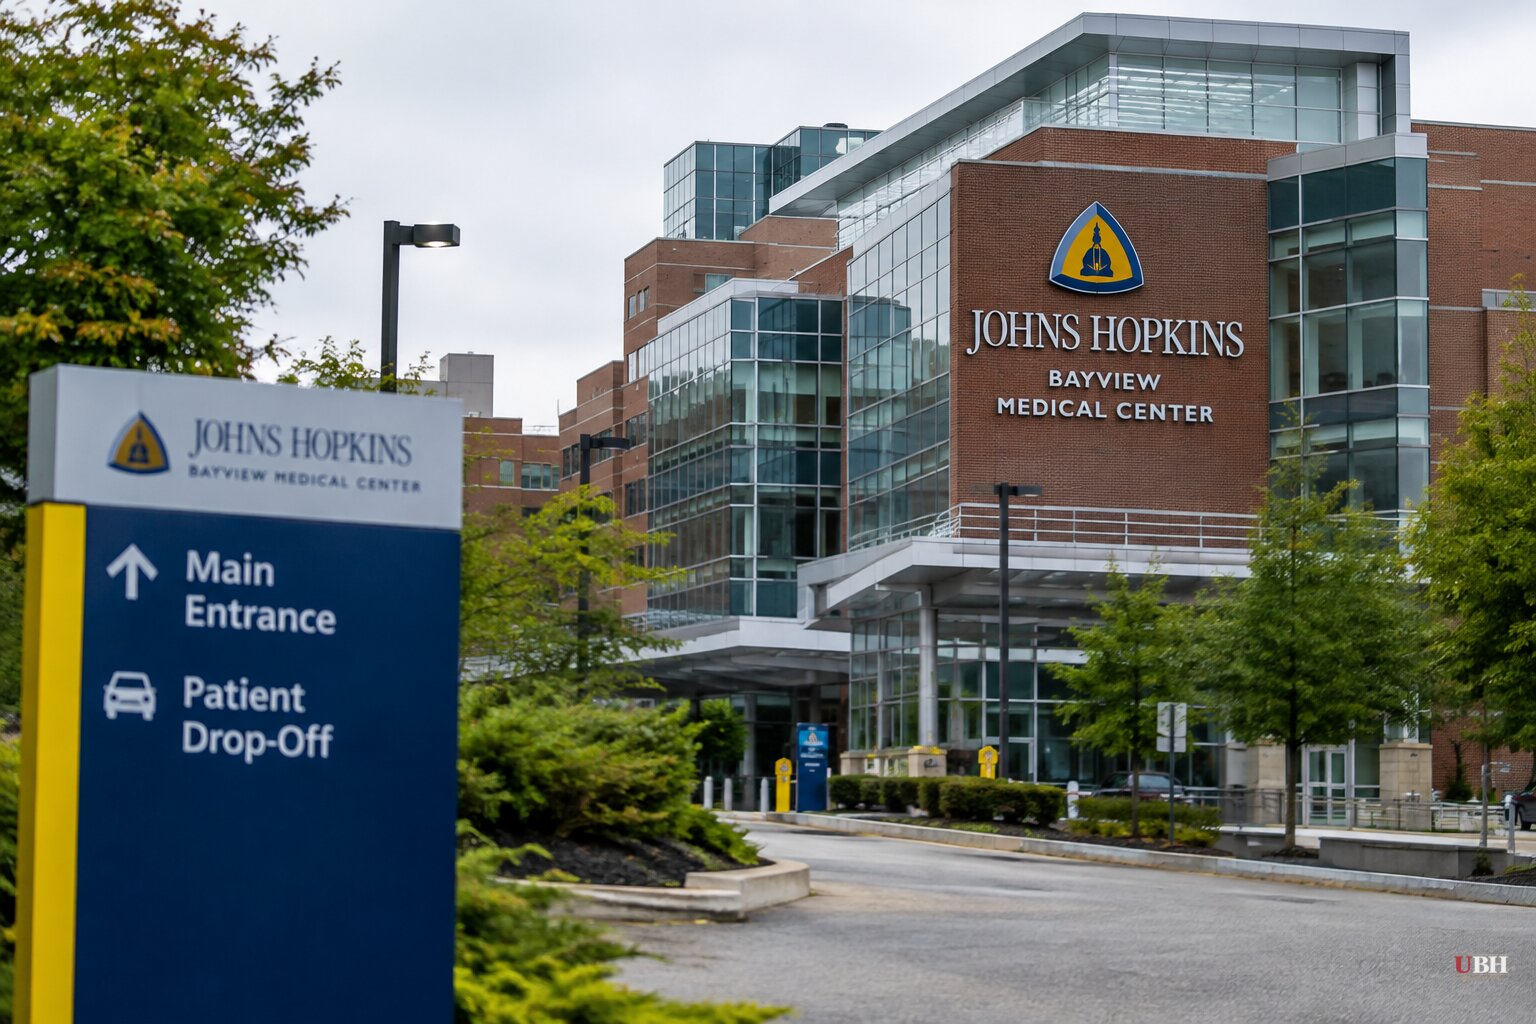
On Sept. 21, a worker at Johns Hopkins Bayview Medical Center in Baltimore uploaded a spreadsheet covering 3,182 patients to a third-party AI tool Johns Hopkins had not approved. The file held patient names, medical record numbers, treatment information and provider names. Johns Hopkins says it found the incident during an internal review the same day. It began notifying affected patients on Oct. 22.
In an emailed statement, the health system said it had the employee delete the original prompt, the thread and the document from the tool's history. It also contacted the company that operates the tool to request deletion and put in place "corrective measures to prevent similar incidents." The statement describes a request for deletion, not a confirmation that the data is gone from the vendor's systems.
Most health organizations can't see their own AI
The Hopkins case is one incident. Surveys suggest the underlying problem is broad.
Clearwater Security surveyed 150 health systems, health plans and tech firms for its 2026 Healthcare AI Benchmark Study. It found 91% cannot verify what AI is running inside their organizations. Only 14% say they verify their vendors' safeguards around AI use.
"I was a little surprised by the numbers," Clearwater president Baxter Lee said, adding that the 91% figure points to "a big gap in terms of really understanding how AI is being deployed." Lee said third-party risk was already a long-running challenge, and AI adoption among vendors adds to it. Hospitals deal with hundreds of vendors.
DNSFilter, a security firm, reached similar conclusions in a June 2026 survey. Its healthcare sample was only 30 IT and cybersecurity professionals, drawn from a 400-manager survey across industries, so treat the figures as indicative, not definitive.
Within that group, 70% said their organizations have AI policies, but only 40% said they enforce them consistently, which DNSFilter says is the lowest of any sector it surveyed. At 47% of healthcare organizations, employees can authorize a new AI tool to access company systems without higher-level approval.
Twenty-seven percent said they knew of unauthorized AI connections to their platforms. Another 23% suspected it but couldn't prove it. One in 10 said an unapproved AI tool had already led to a cybersecurity incident.
Monitoring is thin too. Only 27% said they were confident they monitor all their security tools, and four in 10 monitor fewer than half. Six in 10 rely on their AI and SaaS vendors to tell them about incidents, versus 43% in other sectors DNSFilter has surveyed. "A tool nobody is watching can't raise an alert," DNSFilter said.
There is a confidence problem as well. Eighty-seven percent of the healthcare respondents said they could detect a breach within six hours.
Why staff go around IT
The people using these tools are not, for the most part, trying to cause harm. They are trying to get through the workday.
Joel Selanikio, a pediatric attending physician at Georgetown University Hospital, told Digital Health Insights that "the phone in your pocket is almost invariably eons beyond any IT that's being used in the hospital." A 2025 Offcall report found 81% of physicians were unhappy with the pace of their employer's AI adoption.
That is the strongest counterweight to a simple crackdown. Clinicians and staff argue the approved tools are slow or missing, and the free ones work. A policy that bans the fast option without supplying a good alternative invites the behavior it prohibits.
The problem is not limited to chatbots. Nelson Advisors, a healthcare advisory firm, lists four forms: consumer chatbots, AI features inside software an organization already licenses, free point tools such as ambient scribes, and browser extensions that can read every page a clinician opens, including the electronic record. The firm argues that hospital AI governance was built around products the organization buys, such as procurement gates and clinical safety cases, and "almost none of that machinery sees the AI that staff bring in through the side door."
Consumer AI platforms are leaking too
Outside hospitals, the same dynamic is playing out at scale. Security researchers at Claroc disclosed in November that 35,578 of 37,571 apps built with xAI's Grok app builder were publicly accessible without authentication, according to a write-up by security vendor Aviatrix. The cause was a default "Anyone with the link" access setting plus subdomains discoverable through passive DNS enumeration.
The exposed material included plaintext employee password lists and a hospital ICU patient briefing, Aviatrix says. It adds that SpaceXSI removed its 24 internal staff apps but did not proactively notify other affected organizations, leaving hundreds of exposed apps online at the time of publication. Aviatrix sells security products, and these details come from its summary of the researchers' findings.
What's next
Johns Hopkins has not said whether the AI vendor has confirmed deletion of the Bayview file. Clearwater says it intends to track its 2026 results as a baseline for future surveys. Whether hospitals can move from having AI policies to enforcing them is the open question. The one measurable test will be how many more breach notices like Bayview's turn up.
In this case, the system caught the mistake within a day. The notices to 3,182 patients took a month.
Sources used for this briefing
7 links from 7 independent newsrooms (syndicated copies of the same report count once)
These are the sources it draws on, linked so you can verify.


