
Unbiased headlines. Facts, not spin.
Unbiased Headlines is an independently owned news organization. We bring you the facts, not opinions, written fresh from 110+ named sources. Sources linked so you can verify it yourself.
 tech
Major Story (8/10)
Bloomberg Investigation Links Russia-Tied Hackers to Burst Pipes, Spoiled Meat and Factory Fires in About 20 Countries
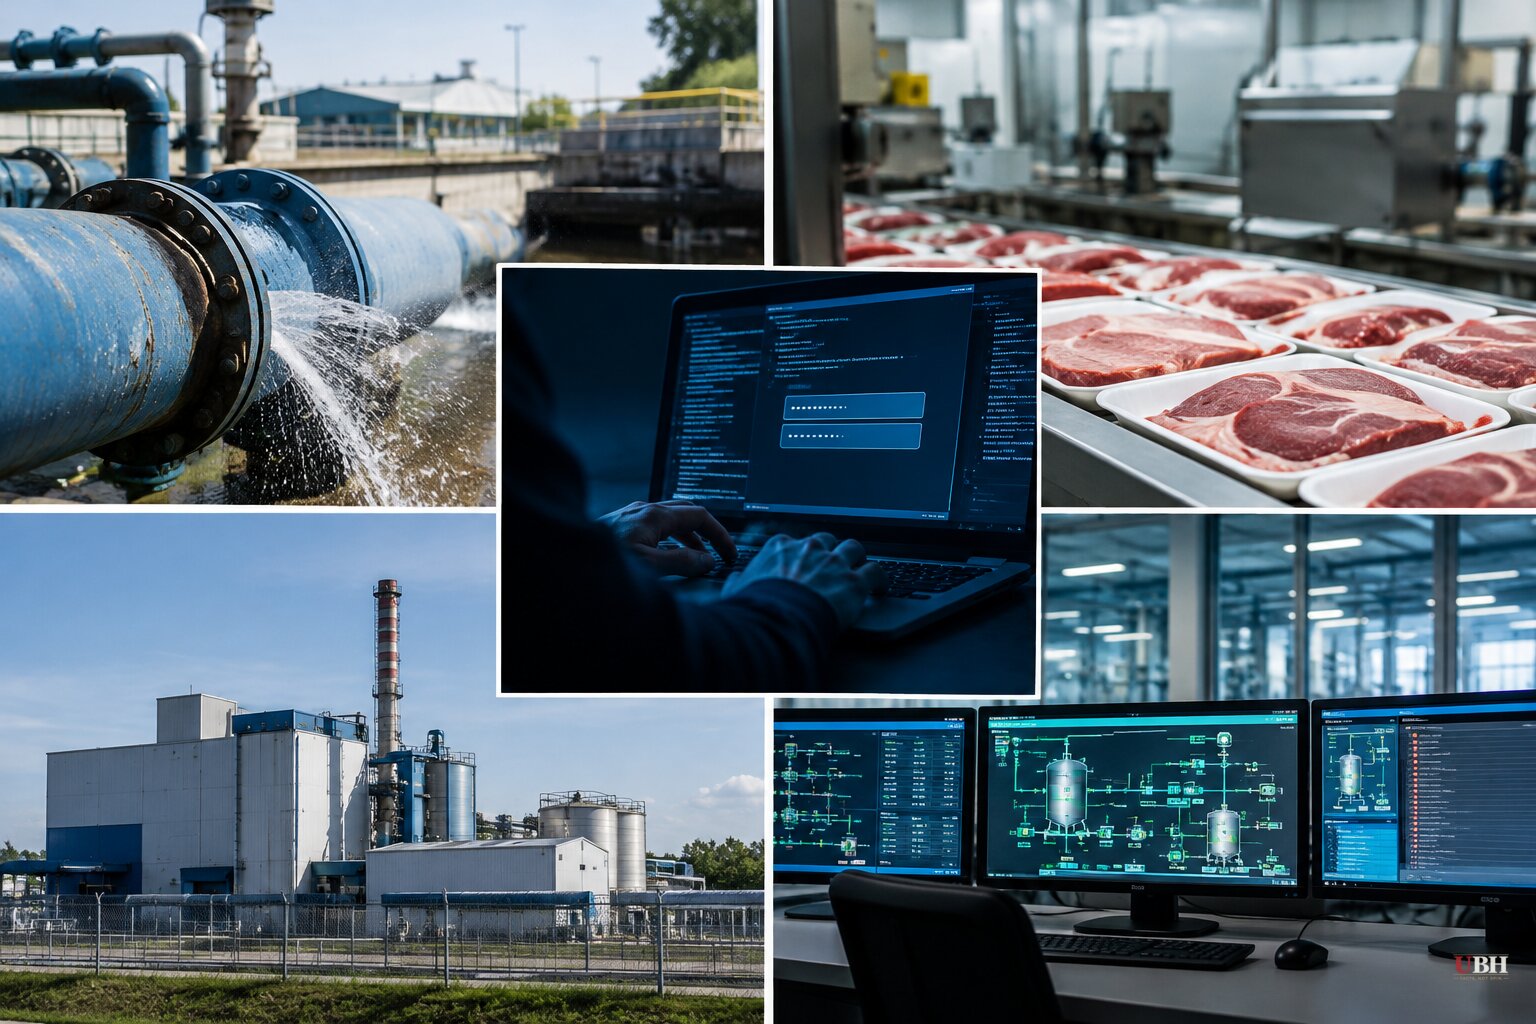
A Danish village pump house, a meatpacking plant near Los Angeles and a Spanish factory share the same weakness. Each was reportedly breached through an industrial control system left on the public internet and protected by a weak or default password.
That is the central finding of a Bloomberg investigation published Oct. 27. It describes a campaign that moved from knocking websites offline to causing physical damage: burst pipes, spoiled food, chemical leaks and fires.
The Danish pump house with a password of "1234"
In December 2024, a water pump in the Danish village of Tureby began running out of control. The chair of the local water committee found himself locked out of a control panel he normally managed.
Technicians later concluded that someone had connected remotely through an internet-facing industrial control interface. According to the Bloomberg account, the intruder zeroed out the pressure settings and waited for workers to restart the pumps manually. The intruder then surged the pressure until underground pipes burst.
About 450 homes lost water for days. The password was "1234."
What the damage looks like elsewhere
Bloomberg reports the activity began in late 2024 and has hit facilities in about 20 NATO countries. The incidents it describes:
- Spain: a fire at a plant that makes renewable-energy equipment, plus disruptions at wineries and crematoriums.
- California: in November 2024, attackers shut down refrigeration at a meatpacking facility near Los Angeles. More than 2,000 pounds of meat (roughly 900 kilograms) spoiled. An ammonia leak forced workers to evacuate.
- Texas: that same year, attackers changed control settings at a public water system, causing water to overflow from tanks.
The U.S. cases also include an October 2024 break-in at another facility's control system. The details of that incident are not established here.
Who is behind it
Bloomberg attributes the attacks to two groups: the Cyber Army of Russia Reborn, known as CARR, and Z-Pentest, described as an offshoot focused on industrial sabotage. U.S. prosecutors have linked CARR's activities to oversight and funding by Russia's military intelligence agency, the GRU. That is a prosecutors' allegation, not an adjudicated finding.
The groups' own stated intent is on the record. Yulia Pankratova, identified as a CARR representative, said the group will keep targeting hospitals and water systems and recognizes no "red lines." That statement comes from a single secondary account of the Bloomberg report. Hospitals have not appeared in the documented incidents.
An easy attack, which is the problem
The method is not sophisticated. Every documented intrusion relied on industrial control devices connected to the public internet. They ran VNC, a remote-access tool, on its default port, 5900. They were guarded by a weak or default password.
No zero-day exploit or custom malware is described. The attackers found open doors and walked in.
That cuts two ways. A small utility or plant operator can close the hole in an afternoon by taking the device off the open internet, changing the credentials and putting a firewall or VPN in front of it. But the same simplicity means the pool of vulnerable targets is large, and the attackers need only keep scanning until something critical turns up. Meduza's summary of the Bloomberg findings makes that point: the less sophisticated the attack, the more likely persistent probing eventually finds a poorly protected system that matters.
Who pays for the failure
The victims named so far are small. They include a village water committee, a regional food processor and a municipal water system. These operators often have no dedicated security staff. A water committee in a village of a few hundred people is not equipped to run a defense against a state-backed intelligence service.
Still, the failures were basic. Anyone holding a remote-access device that controls pressure valves or ammonia refrigeration is responsible for who can reach it. Government regulators and insurers have also not forced the issue. Bloomberg's account suggests voluntary hygiene has not worked.
What remains open
The sources do not say how many internet-exposed industrial systems remain in Western countries, or whether any government has ordered operators to close port 5900 exposures. Nor do they say whether any individual has been charged over the Tureby, Los Angeles or Spanish incidents.
What is documented is the pattern. Cheap access, physical consequences and a group representative who says the targeting will go on. Whether utilities lock their doors before the next pump runs away is up to the people who own the panels.
Sources used for this briefing
5 links from 4 independent newsrooms (syndicated copies of the same report count once)
These are the sources it draws on, linked so you can verify.


