
Unbiased headlines. Facts, not spin.
Every story is an unbiased news briefing written from 110+ sources across the spectrum — sources linked so you can verify it yourself.
 tech
Notable (6/10)
August 11, 2026 at 07:50 PM
Zoom Patched a Screen-Share Bug That Let One Meeting Participant Hijack Another's Device With Zero Clicks
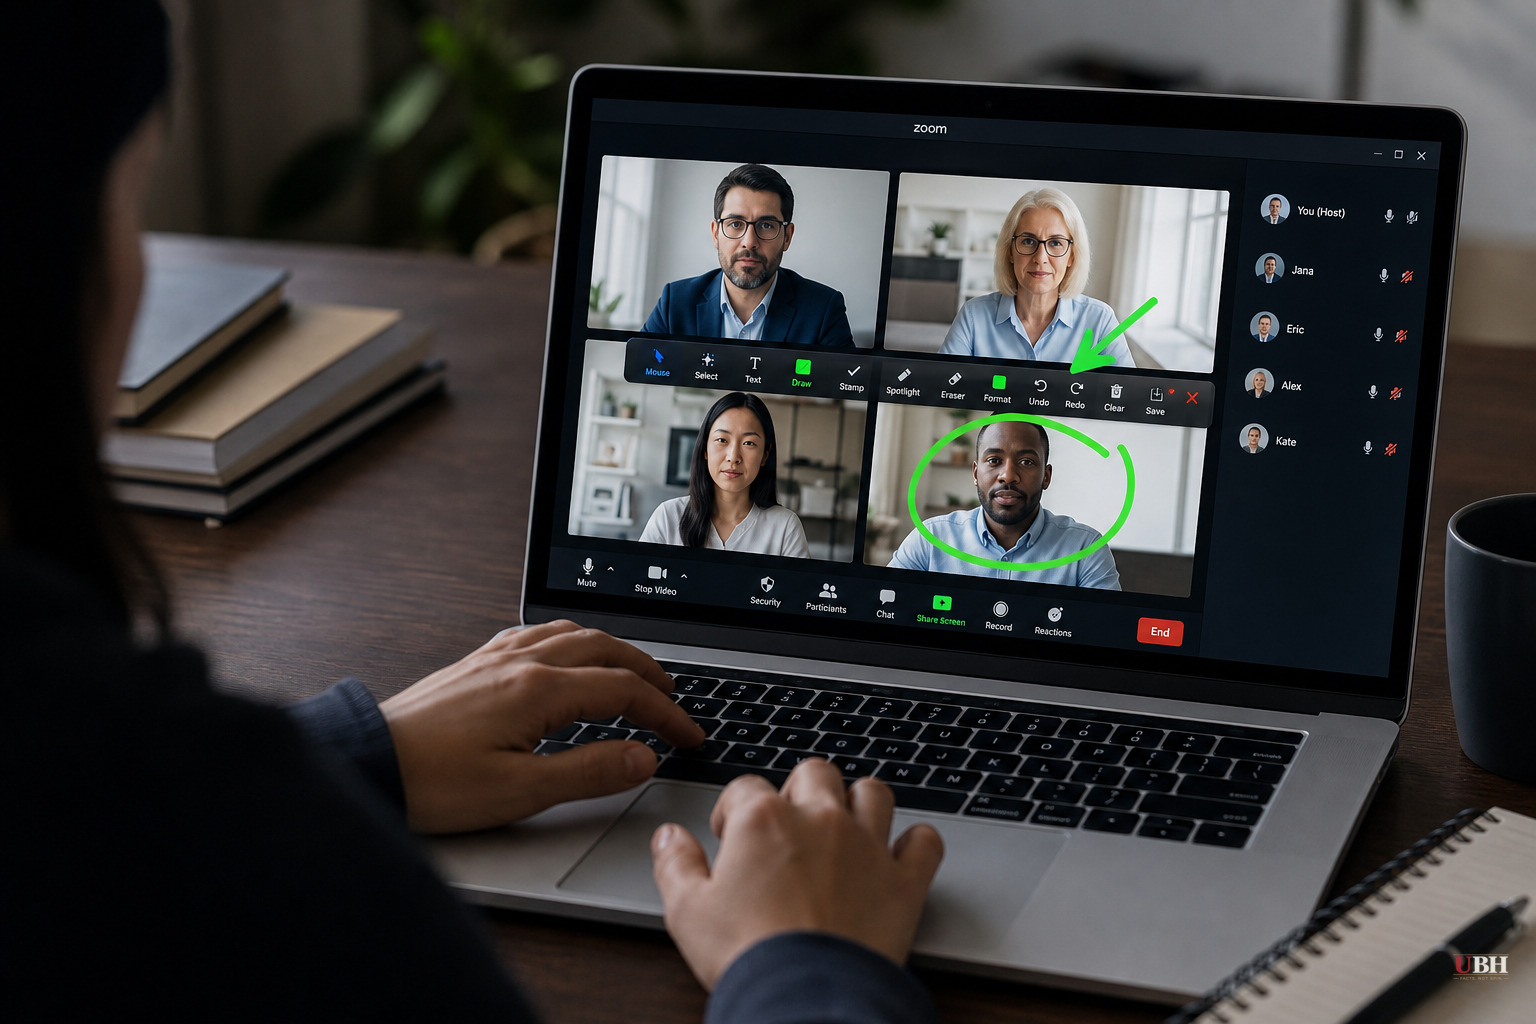
Zoom's screen-sharing annotation tool, the little feature that lets people draw arrows and scribble notes on a shared screen, had a hole in it big enough to let one meeting participant take over someone else's computer. No click. No download. No warning on screen. Just join the call.
That's according to A Security, an Israeli-founded offensive-security startup, which disclosed the vulnerabilities publicly this week. Zoom issued a security advisory the same day, confirming fixes across Windows, macOS, Linux, iOS, and Android, according to Wired.
A Security researcher Idan Levcovich found the bug on June 8 while analyzing Zoom's Android client, according to CyberInsider. A working exploit against Zoom version 7.0.5 was confirmed the next day. The firm reported it to Zoom privately on June 10. Zoom acknowledged it within a day and started shipping client and server fixes weeks later, PCMag reported. The public writeup didn't drop until August, roughly two months after the patches were already out.
That gap matters. thehackernews.com noted that client fixes shipped in June and July, and no exploitation has been reported as of publication. None of the three vulnerabilities appear in CISA's Known Exploited Vulnerabilities catalog. This was a real bug, but nobody has evidence anyone actually used it to hack a real person.
How the bug actually worked
The vulnerable code lived in libannotate.so, the native library that handles Zoom's drawing and annotation features, according to CyberInsider. Instead of sending your scribbles as a picture, Zoom packages them into structured data objects and sends them through its meeting infrastructure to be rebuilt on the other end.
The parser trusted numbers the sender supplied about how much data was coming, without properly checking those numbers against the size of the buffers meant to hold them. One flaw, CVE-2026-53413, involved a fixed 128-byte buffer that could be overflowed with an oversized count value, letting an attacker overwrite adjacent memory and potentially hijack program execution. Researchers demonstrated this on macOS by getting a victim machine to launch Safari on command, according to CyberInsider.
A second flaw, CVE-2026-53414, was a buffer over-read that could crash a participant's client or expose uninitialized memory. A third, CVE-2026-53415, was a use-after-free bug. Zoom tracks them under security bulletins ZSB-26015, ZSB-26016, and ZSB-26017.
The dispatcher problem made it worse. Every viewer in a meeting holds a channel to whoever is sharing their screen, and the sharer holds a return channel meant only for acknowledgments. According to thehackernews.com, the system didn't check which channel a message actually came from before processing it, meaning a message meant to flow one way could be sent the other way and still get processed as if it were legitimate. That's what let the attack run in both directions: a compromised presenter could reach every viewer, and any viewer could reach the presenter.
The AI claim deserves scrutiny, not just repetition
A Security says it went from discovery to a working exploit in under 24 hours using fewer than 20 prompts on publicly available AI models. Cofounder Omer Gull told Wired that a job that used to take a five-person team six months now takes a fraction of that time. "The barrier to entry is dropping rapidly," Gull said.
Most outlets covering this story, including Engadget, PCMag, and 9to5Mac, repeated it largely at face value. But thehackernews.com pushed back on parts of it. The firm's writeup names no specific AI model, so nobody outside the company can independently verify the claim. Zoom itself rates the bugs lower in severity than A Security does, and Zoom's own advisories mark user interaction as required for all three vulnerabilities, which sits awkwardly next to A Security's "zero-click" framing. A Security also rates all three flaws at 9.0 under CVSS 4.0, a score that appears nowhere in Zoom's actual bulletins, which use the older CVSS 3.x scale with scores of 8.3, 6.5, and 8.3.
None of that means the bug wasn't real or serious. It was real, and Zoom's own advisory confirms remote code execution was possible. It does mean the marketing layer on top of the research, the "nation-state weapon in a day" framing, is coming from a company that just raised $37 million and has an obvious incentive to make its capabilities sound as dramatic as possible.
What's actually resolved and what isn't
The fix is straightforward: update to Zoom Workplace 7.1.5 or 7.0.6 or later, according to PCMag and Zoom's own security bulletins. Running an old version is exposure, not proof of compromise, since the researchers didn't identify any known indicator of past exploitation, according to Gridinsoft.
What's unresolved is bigger than Zoom. If a well-funded but relatively small research team really did compress a nation-state-caliber exploit timeline from six months to a day using tools anyone can access, that's a claim the broader security industry, not just Zoom, needs to independently test and confirm, not take on one company's word.
Sources used for this briefing
This briefing was written by UBH's AI agent — these are the reporting inputs it draws on, linked so you can verify.


