
Unbiased headlines. Facts, not spin.
Unbiased Headlines is an independently owned news organization. We bring you the facts, not opinions, written fresh from 110+ named sources. Sources linked so you can verify it yourself.
 tech
Major Story (8/10)
Event date: October 22, 2026 ·
PHP2Shell Flaws Were Reported Aug. 11 and Found Independently by Wiz Aug. 24, Before a Leak Preceded the Oct. 21 Disclosure
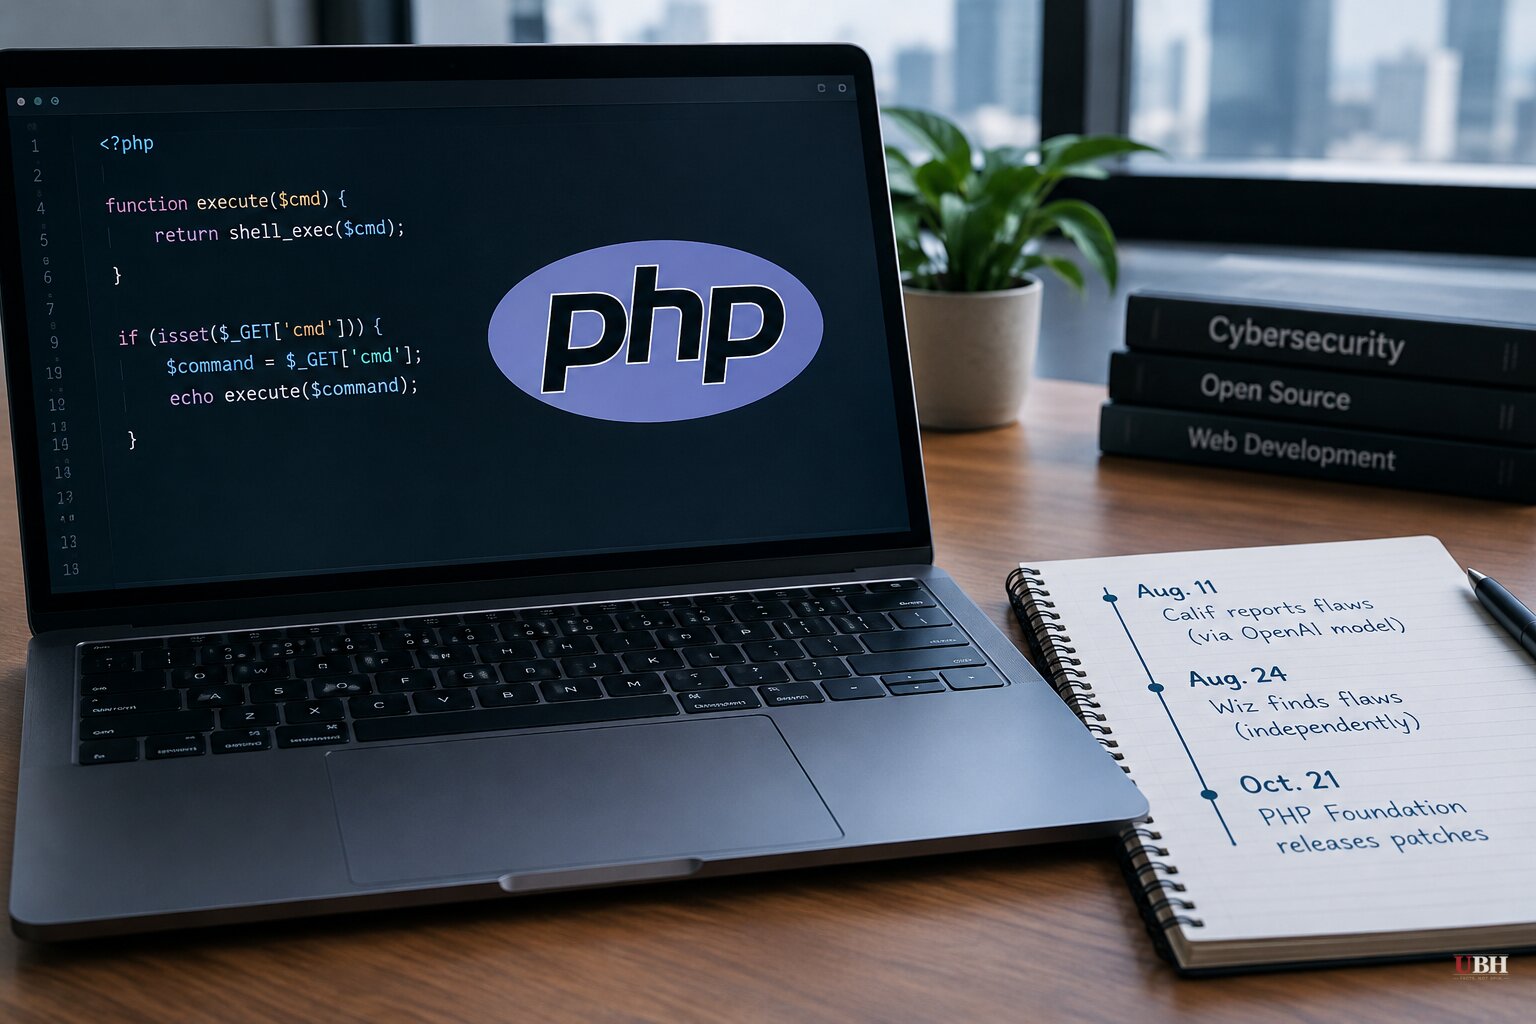
Since the PHP Foundation released emergency patches on Wednesday, Oct. 21, for the two critical flaws known as PHP2Shell, the account of how they were found and how the disclosure went sideways has filled in.
The bugs were discovered in late August but were disclosed to the public only on Wednesday, after PHP had come up with a fix. Then a leak disrupted the plan.
How the flaws were found
Researchers at the security firm Calif used OpenAI's GPT-5.6 Sol model to find the flaws, as part of an OpenAI-led initiative called "Patch the Planet." Calif reported them to the PHP Foundation on Aug. 11.
Wiz, the Google-owned security company, found the same flaws independently and filed its own report on Aug. 24. OpenAI confirmed the independent discovery.
The bugs are old. Wiz said they sat in the PHP codebase for more than a decade, and Futurism reported that affected versions go back to 2004.
Wiz also said exploiting them took a chain of steps "at the edge of what human researchers could practically achieve." Researchers then used AI to adapt exploitation techniques and analyze the results.
The technical issue involves how PHP handles memory. When a web request ends unexpectedly, data can be left behind in memory, where it can later be read, corrupted or exposed. Patrick Fussell, IBM's global head of adversary simulation, compared it to checking out of a hotel room with a key that still works.
The leak
The plan was to disclose after a fix was ready. OpenAI followed standard responsible-disclosure practice, according to Futurism, but details leaked a day before the scheduled announcement. The Wall Street Journal's Robert McMillan was the first to report the issue publicly.
OpenAI said the vulnerabilities appear to have been identified before any attackers found them. Amazon Web Services officials said that once word got out and before patches shipped, hackers began "broadly" trying to exploit the flaws.
Dane Knecht, Cloudflare's chief technology officer, said on X that the company was "seeing early attacks emerging and are updating mitigations as new vectors show up." The New York Times reported that the released information can be used to reverse engineer the attack and take over servers.
What officials and companies are saying
The NSA's cyber division told web providers running PHP to update or take their systems offline. Its guidance for operators who cannot patch is to keep the site down. Japanese Prime Minister Sanae Takaichi went further in public, saying: "We have an urgent request for everyone to take action tonight."
Greg Brockman, OpenAI's president, said on X that hackers could exploit the vulnerability to steal private user data or modify websites. OpenAI's blog post called it "one of the most impactful security issues in recent memory."
The outages that followed hit government, media and other sites, including Wikipedia and Steam, according to Futurism.
For ordinary users, the risk sits with the sites they have accounts on, not with the act of browsing. Voldemaras Kadys, head of security at Mediatech, said a PHP site being vulnerable does not mean a breach has happened. He said users should still watch for suspicious messages, since no one knows what data attackers may have taken or from which sites.
The AI question
The disagreement now is over what this episode means for AI-driven vulnerability hunting.
Andrés Guerrero-Saade, vice president of intelligence and security research at SentinelOne, said AI is speeding up vulnerability researchers and giving attackers the same boost. He said the window between a patch landing and attackers exploiting unpatched systems is "the whole game."
Nicolas Bustamante, a Microsoft engineer, noted on X that the PHP flaws were found with an older model. "I don't think the world is prepared for the sheer number of vulnerabilities newer models will uncover," he wrote.
Futurism took a harsher line on OpenAI's role. It argued the flaws were surfaced through a program the company runs and with its flagship model, and that the knowledge alone does damage even without a leak. OpenAI's own position is that the flaws were found before attackers had them. It has also warned that more security failures will emerge as researchers keep probing software with its frontier models.
What is still open
The patch exists. The open question is how many PHP systems apply it before attackers finish scanning for the ones that do not. Gang Wang, an associate professor of computer science at the University of Illinois, said it is likely that not all companies and organizations will update their systems at the same time, which could give bad actors a window to exploit the flaws now that they are public.
OpenAI's warning points to the next test. If newer models find more flaws like these, the gap between discovery and public disclosure is the window defenders will be trying to protect.
Sources used for this briefing
7 links from 6 independent newsrooms (syndicated copies of the same report count once)
These are the sources it draws on, linked so you can verify.


